Manufacturing
Supplier wire fraud and the physical path to the line.
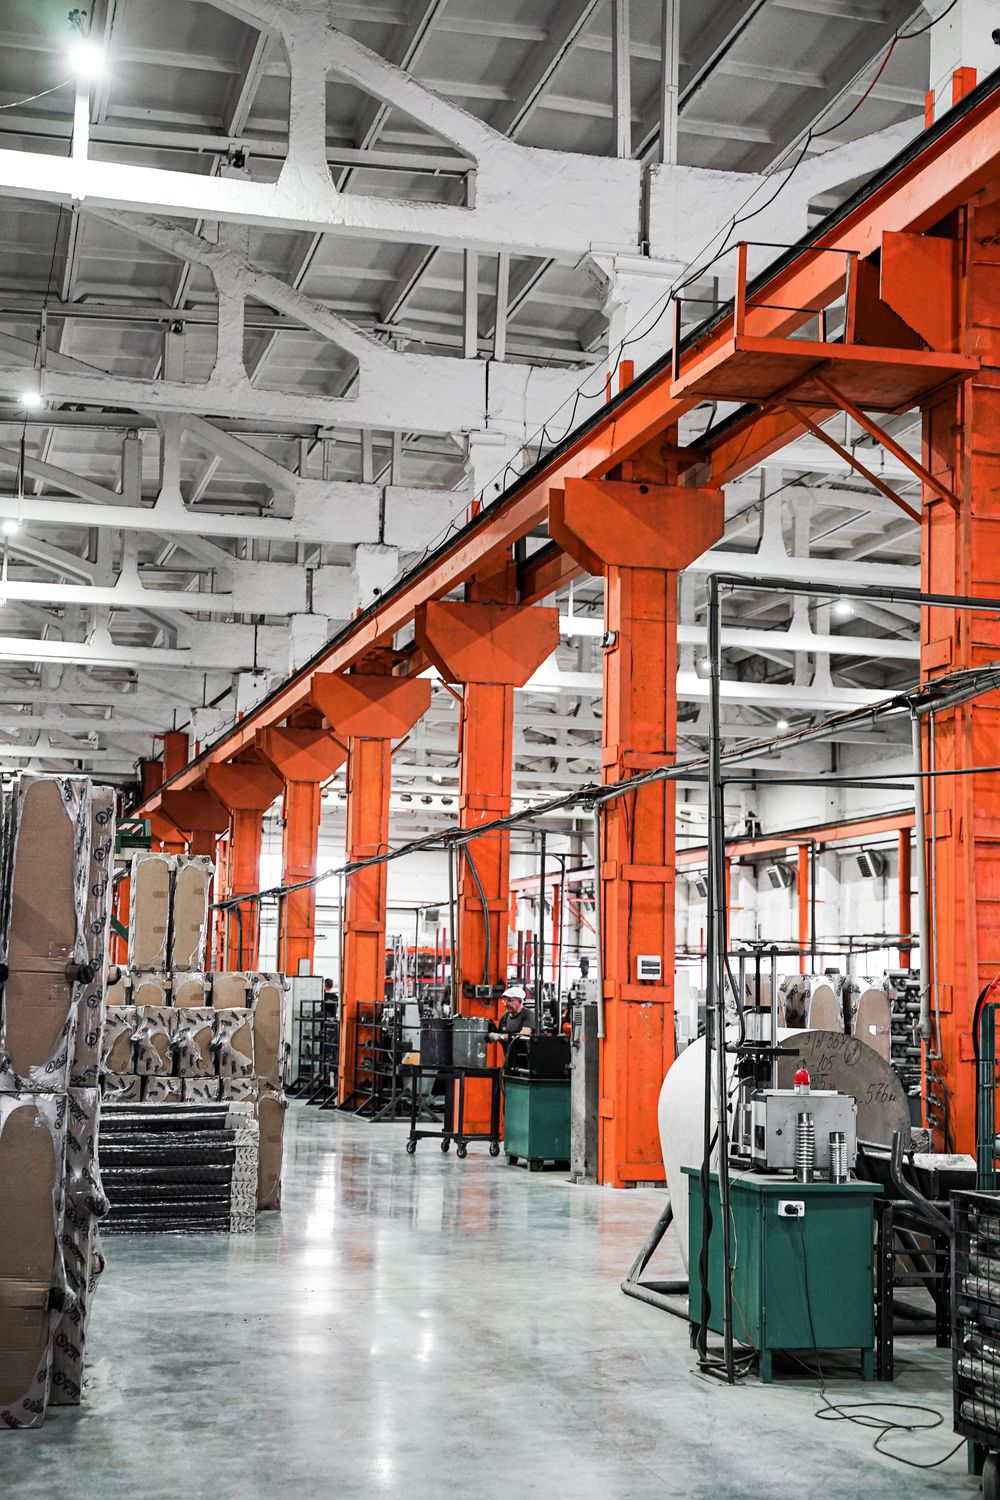
A plant runs on schedule and momentum. A delayed shipment stops a line; a late supplier payment risks raw material delivery. Attackers exploit that operational pressure because factory floors and procurement desks are conditioned to solve problems quickly rather than verify them slowly.
Vulnerabilities We Test
Out-of-Band Payment Verification Gaps
Determining whether accounts payable will update banking, account, or remittance details based on urgent vendor correspondence without using a verified, pre-established phone callback.
Loading Dock and Contractor Ingress
Testing whether exterior bay doors, contractor staging areas, and maintenance gates allow an unbadged visitor to bypass the main lobby and enter operational facilities unnoticed.
Shop-Floor Terminal Custody
Evaluating whether active workstations connected to production scheduling, inventory management, or industrial networks are left unlocked and accessible during shift changes and lunch breaks.
Executive Pretexting Under Operational Pressure
Measuring whether plant controllers, warehouse managers, or purchasing leads will bypass standard authorization procedures when contacted by someone impersonating corporate leadership during an operational disruption.
Logistics & Supply Chain
Rerouted freight, compromised dispatch, and fast-moving money.
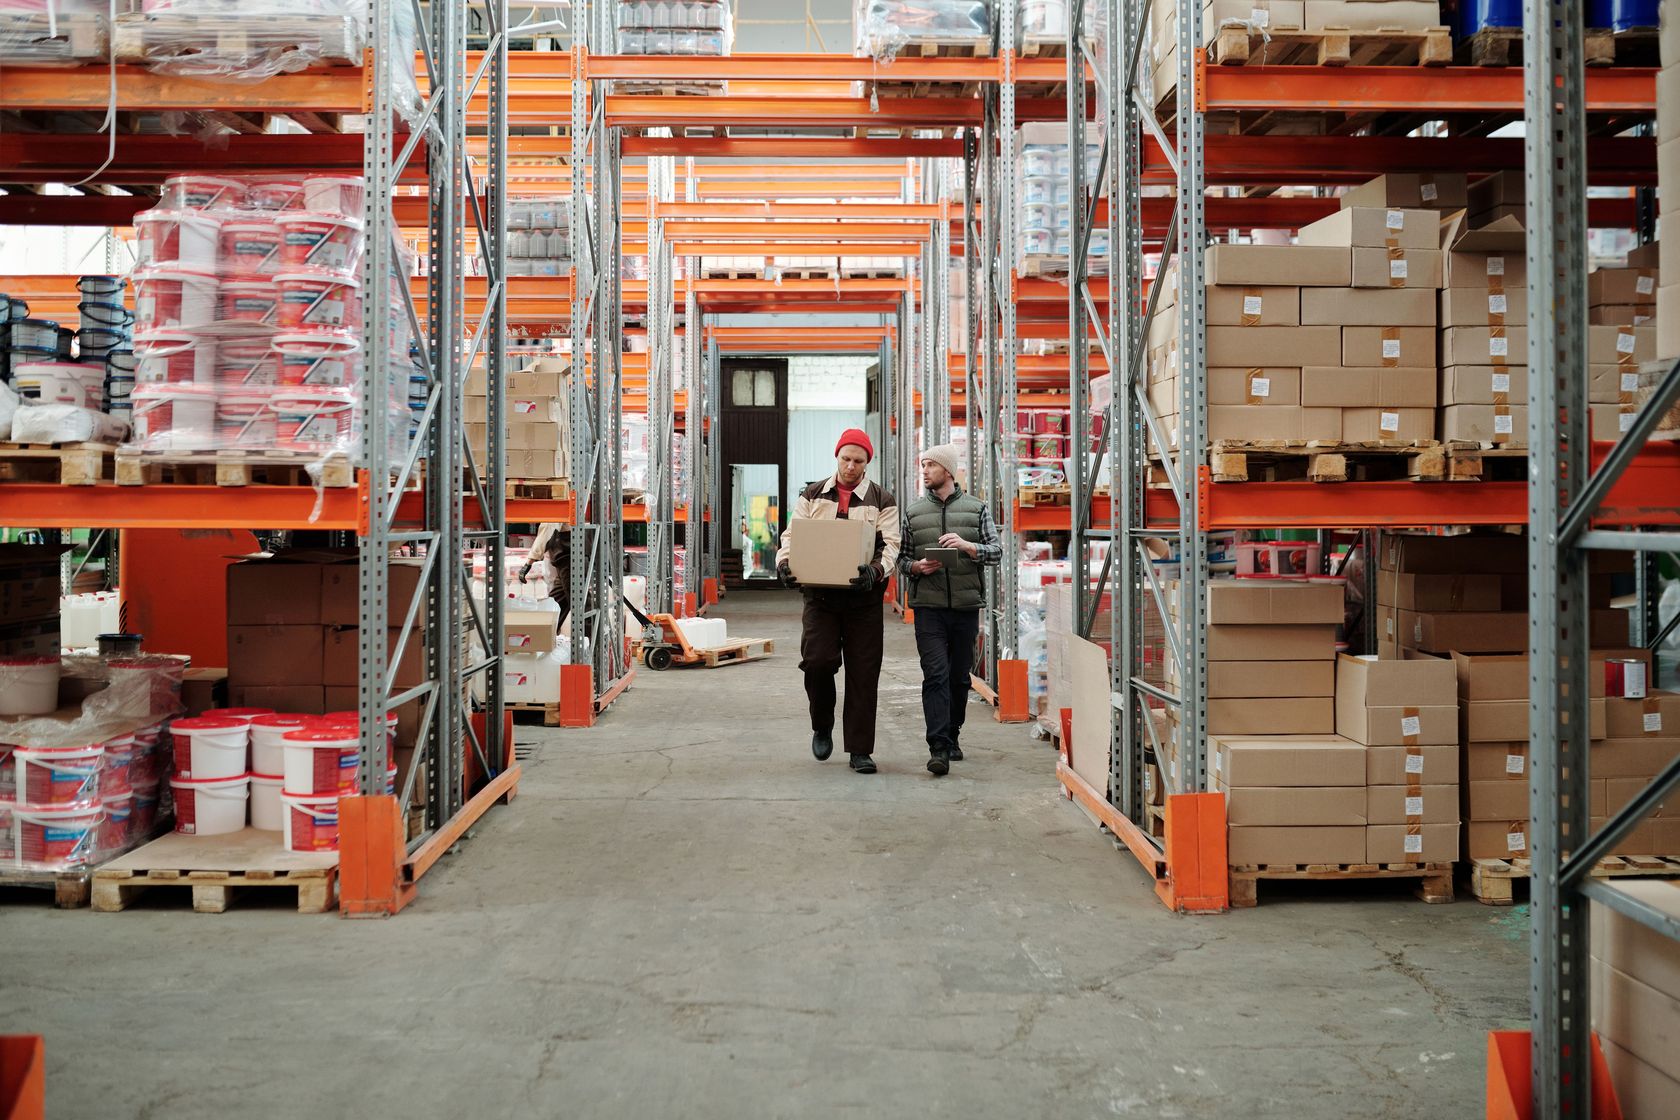
Dispatchers manage hundreds of phone calls, texts, and emails every shift. Drivers arrive on razor-thin turnaround windows. When speed is the only metric that matters, stopping to authenticate a voice on the phone feels like slowing down the company.
Vulnerabilities We Test
Load Redirection and Release Breakdowns
Testing whether dispatchers or warehouse clerks will change a delivery address, transfer release authority, or modify carrier assignments over an incoming call or unauthenticated email without formal verification.
Quick-Pay and Factor Account Diversion
Measuring whether accounting staff will update carrier direct deposit or factoring company details under the pressure of paying out a driver immediately upon delivery.
Yard and Staging Security Failures
Evaluating whether unescorted visitors can walk past dispatch counters, enter driver lounges, and access manifest clipboards, bill-of-lading copies, or internal yard keys.
Dispatch Account Reset Procedures
Testing whether your internal IT or third-party help desk will reset user credentials or re-register an MFA token for a remote dispatcher on an unverified inbound phone call.
Commercial Real Estate
High-stakes closings, temporary trust, and irreversible wires.
A commercial real estate closing is a chaotic network of brokers, lawyers, lenders, and buyers who rarely have an established working relationship. Everyone expects wire instructions to change or finalize near the deadline. An attacker does not need to crack encryption; they just need to introduce new banking details while everyone is watching the clock.
Vulnerabilities We Test
Closing-Day Wire Instruction Updates
Determining whether law clerks, financial managers, or closing coordinators will accept revised wiring details without requiring live, dual-channel voice verification on an independently verified phone number.
Deal-Lead Impersonation
Evaluating whether finance and accounting teams will execute significant deposit transfers or operational disbursements when pressured by someone impersonating an acquisitions partner who is "travelling and unreachable."
Property Management Ingress
Testing whether unannounced "inspectors," "appraisers," or "contractors" can bypass on-site property managers and security desks to access mechanical rooms, tenant utility closets, and building management systems (BMS).
Confidential Document Exposure
Measuring whether sensitive leasing rosters, purchase-and-sale agreements, and tenant financial files are left visible in unattended conference rooms, physical file rooms, or open administrative areas.
Professional Services
Confidential client files and the deference paid to seniority.
Law firms, accounting practices, and advisory firms store the strategic plans, patent filings, litigation files, and tax records of their clients. The vulnerability inside these firms is rarely technical; it is cultural. Staff are hired to be discreet and helpful, and junior employees are conditioned never to challenge a partner.
Vulnerabilities We Test
Executive Override Vulnerability
Testing whether administrative assistants, paralegals, or billing clerks will bypass documented security controls when contacted by someone using the name, voice, or authority of a managing partner.
Help Desk Credential Takeover
Measuring whether internal support teams will reset passwords, bypass MFA, or provision access to an off-network laptop without following strict out-of-band identity validation protocols.
Lobby and Conference Floor Tailgating
Evaluating whether an unfamiliar visitor wearing business attire can walk past the reception desk, settle into an empty conference room, and connect to physical wall ports without being challenged or escorted.
Print and Custody Failures
Testing whether confidential client records, tax returns, litigation notes, and partner correspondence are left unattended on central floor printers, mail counters, or shared filing cabinets.
Start here